Feathergrid on Azure and AWS: What Runs Where, and Why
Feathergrid runs on Microsoft Azure and AWS. Azure runs the application and your data. AWS holds only the fingerprints that anchor the tamper-evident record. Here is why it is built that way.
Feathergrid runs on Microsoft Azure and Amazon Web Services, in the United States. Azure runs the application and your data. AWS holds only the fingerprints that anchor Feathergrid's tamper-evident record, never your data. Enterprise customers can also run Feathergrid in their own cloud tenancy.
Here's what runs where, and why it's built that way.
Why use two clouds at all?
For the record.
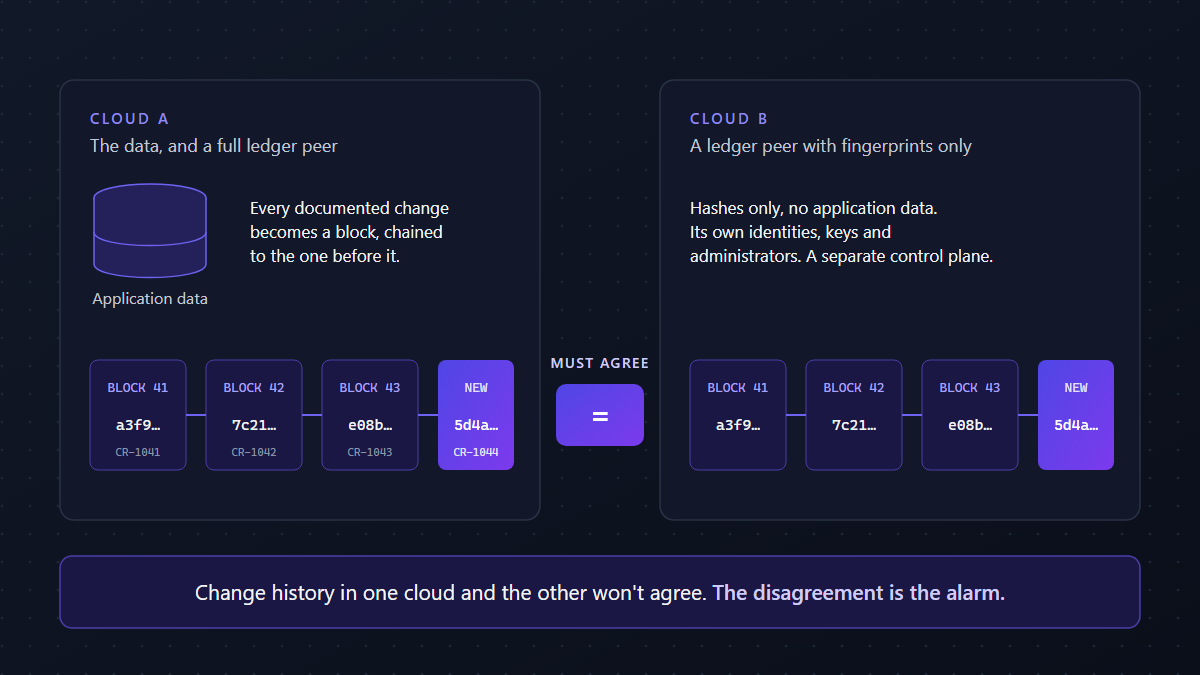
Most software keeps its history in one database. Anyone with enough access to that database can change it, and nobody would know. Feathergrid takes a different approach: every entry in its record gets a cryptographic fingerprint, and those fingerprints are anchored in a second cloud run by a different company.
Change an entry in one cloud and it stops matching its fingerprint in the other. A disagreement between the two raises an automatic alert. If the record and the ledger are in conflict, Feathergrid triggers a rollback to the backup database.
That's what "tamper-evident" means here: edits show.
What runs on Azure?
The application and your data.
- Where: Microsoft Azure, in the United States.
- Your data: processed and stored in the US, encrypted in transit and at rest, kept separate for each organization, and never used to train AI models.
- Keys: held in Azure Key Vault hardware security modules validated to FIPS 140-3 Level 2.
AWS holds only the fingerprints that anchor Feathergrid's tamper-evident record, never your data.
What runs on AWS?
Only the fingerprints that anchor the record. No application code and no customer data.
Keeping your data in one cloud and only fingerprints in the other also keeps the compliance boundary small. There's one place your data lives, and one place to review.
Can we run Feathergrid in our own cloud?
Yes, on the enterprise plan. Enterprise customers can run Feathergrid in their own cloud tenancy. Start with a pilot: 4 to 8 weeks, scoped against your own systems.
What about the edge?
Sensor data is collected at the edge through a gateway, and correlation and dispatch can run on-site. If the connection drops, Feathergrid keeps working from the latest picture it has. More in Feathergrid at the Edge.
Where does Feathergrid stand on compliance?
Plainly:
- FedRAMP: not authorized today. Feathergrid is built to run inside a partner's authorized environment.
- Experience: our founder has taken architectures through HIPAA and FedRAMP High audits.
The architecture page walks through the design, including a C4 diagram, and the government page covers teaming with primes.
The short version
Azure runs the application and your data. AWS holds only fingerprints. Change history in one and it stops matching the other. Enterprises can run it in their own cloud. And the edge keeps working when the connection doesn't.
Topics